AVAYA DOCUMENTATION CENTER
Find answers to your technical questions and learn how to use our products
Administering Avaya G450 Branch Gateway
Network security using access control lists
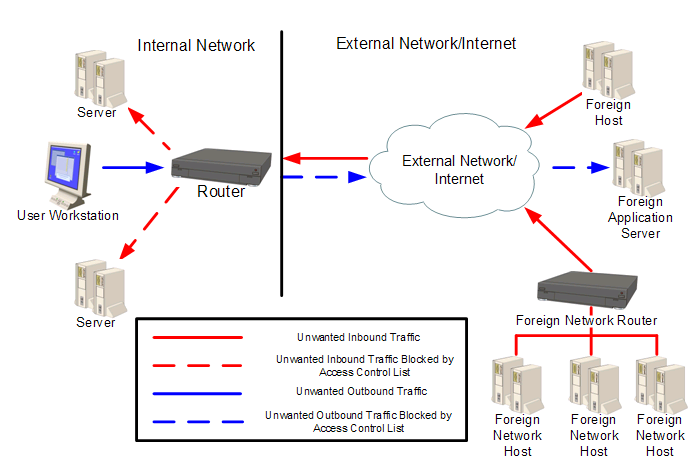
The primary use of access control lists is to act as a component of network security. You can use access control lists to determine which applications, networks, and users can access hosts on your network. Also, you can restrict internal users from accessing specific sites or applications outside the network. Access control lists can be based on permitting or denying specific values or groups of IP addresses, protocols, ports, IP fragments, or DSCP values. The following figure illustrates how access control lists are used to control traffic into and out of your network: