

AVAYA DOCUMENTATION CENTER
Find answers to your technical questions and learn how to use our products
IP Office Security Guidelines
ID Certificate Distribution using Simple Certificate Enrollment Protocol (SCEP)
Each IP Office is configured with the location of the SCEP server along with a password. The IP Office will periodically perform a CSR until it obtains its identity certificate. The private key is kept internally. The SCEP server must be administered to accept the signing request and issue the correct certificate.
As part of the enrollment process the CA certificate used to sign the SCEP request is placed into the TCS after which the IP Office will trust any other certificate signed by that CA. This is the mechanism used in IP Office branch deployments with System Manager (SMGR).
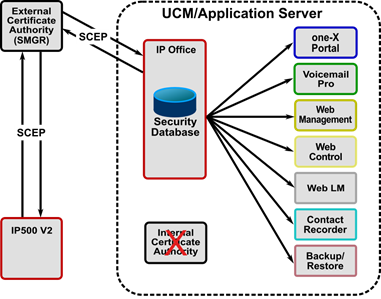
In all cases (External CA, Internal CA, SCEP), when a new identity certificate is received by IP Office, all relevant interfaces/applications are updated.
For more information on creation of a PKI based on SCEP, see Implementing IP Office PKI.