

AVAYA DOCUMENTATION CENTER
Find answers to your technical questions and learn how to use our products
IP Office Security Guidelines
Message Authentication
Message authentication ensures that all data sent by either the system or IP Office Manager cannot be tempered with (or substituted) by anyone else without detection. This involves the originator of the data producing a signature (termed a 'hash') of the data sent, and sending that as well. The receiver gets the data and the signature, and checks both match.
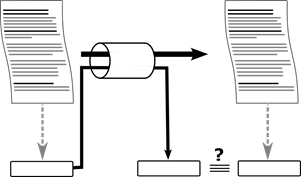
Any data sent may be optionally authenticated using a number of well-known and cryptographically secure algorithms:
|
Algorithms
|
Effective hash size (bits)
|
Use
|
|---|---|---|
|
MD5
|
128
|
Not supported – insufficient strength
|
|
SHA-1
|
160
|
'Low/Medium' security for message authentication.
|
|
SHA-2
|
224, 245, 384, 512
|
'Strong' security
|
In general the larger the hash size, the more secure the signature. However, smaller hash sizes usually incur less processing. IP Office supports message authentication using Transport Layer Security (TLS v1.0, v1.1, and v1.2), Secure Shell (SSH v2), Secure RTP (SRTP) and IPsec protocols.