AVAYA DOCUMENTATION CENTER
Find answers to your technical questions and learn how to use our products
Administering Avaya G430 Branch Gateway
Typical DNS resolver application – VPN failover
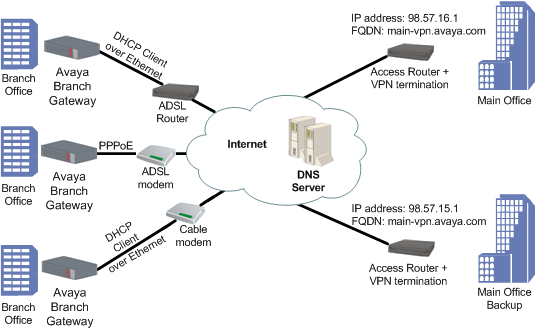
In this typical application, the DNS resolver feature is used to provide a VPN failover mechanism between two main offices. The failover mechanism is implemented as follows.
The VPN branch office(s) connect to two main offices (the VPN remote peers) that are configured with the same FQDN name, but have different IP addresses. When a branch office makes a DNS query to resolve the VPN remote peer name to an IP address, it receives a list with the IP addresses of both main offices, selects the first one, and builds a VPN tunnel with it. If the first main office fails, the branch office sends another DNS query, and receives the IP address of the second main office in reply. It will then start a VPN tunnel with the second main office.
Note:
VPN is supported in IPv4 only.