

AVAYA DOCUMENTATION CENTER
Find answers to your technical questions and learn how to use our products
Deploying Avaya Aura® Device Services
Deploying Avaya Aura® Device Services on ASP using Script
Avaya Aura® Device Services provides a KVM OVA that contains the following files and components:
-
Virtual Disk Images qcow2 files:
-
disk1.qcow2
-
disk2.qcow2
-
disk3.qcow2
-
disk4.qcow2
-
-
OVA Descriptor and Packaging Files:
-
.ovf
-
.mf
-
.cert
-
-
Installation and Deployment Scripts:
-
install_vm.py
-
ovf.py
-
Note:
-
Disk encryption is possible using the script-based deployment.
-
Always follow A1SC output for deployment of applications on the host(s). There should never be more than one instance of a specific application on the same host.
-
Deployment of applications MUST be performed one at a time and delete the artifacts prior to deploying the next application.Solution Deployment Manager Client does not support KVM on RHEL 8.10 or KVM on RHEL 9.6 images for a virtualized environment.
Before you begin
-
Install ASP R6.0.x (KVM on RHEL 8.10) or ASP R7.0.x (KVM on RHEL 9.6)..For more information, see Installing the Avaya Solutions Platform 130 Series at https://support.avaya.com/css/public/documents/101091802.
-
Download the Avaya Aura® Device Services KVM image from PLDS to your computer.
-
Login to the ASP CLI with custadm credentials.
-
Ensure that the staging folder exist:sudo ls -ld /var/lib/libvirt/staging
-
Ensure to remove the older images from the staging folder.
-
Ensure sufficient space is available in the staging folder to copy the KVM image.
-
If the staging folder does not exist, create it using the following commands:
-
sudo mkdir /var/lib/libvirt/staging
-
sudo chown custadm:wheel /var/lib/libvirt/staging
-
-
The chown command now allows custadm to write into the staging directory with sudo. For example, the permissions should look as follows:
drwxr-x---. 2 custadm wheel 6 Oct 23 14:32 /var/lib/libvirt/staging -
Copy the Avaya Aura® Device Services KVM image to the ASP host in /var/lib/libvirt/staging using winscp and custadm credentials.
-
Ensure you are logged into the ASP CLI. If not, login to the ASP CLI with custadm credentials.
-
Run the following command to verify the Avaya Aura® Device Services KVM image is available in the staging folder:sudo ls -lr /var/lib/libvirt/staging
-
Ensure that the required network bridges are configured during the KVM deployment. For example, Management VM Network.
- Log in to the ASP CLI as a custadm user and verify the ASP version using the following command: swversion
- Go to the staging folder;
ADDITIONAL INFORMATION:sudo cdcd /var/lib/libvirt/staging
- Do the following:
-
ASP is on R6.0.0.0ASP is on R6.0.0.1
-
Run the following command to extract the OVA file:
-
Run: sudo tar -xvf aads-kvm-*.ovaKVM OVA extracts the following files:
-
aads-*.ovf
-
aads-*.mf
-
aads-*.cert
-
install_vm.py
-
ovf.py
-
disk1.qcow2
-
disk2. qcow2
-
disk3.qcow2
-
disk4.qcow2
-
-
-
Run the following script to deploy Avaya Aura® Device Services:sudo python3 install_vm.py
Run the following script to deploy Avaya Aura® Device Services: installVM aads-kvm-*.ovaASP completes the auto-verification to ensure the following files are available:
 aads-*.ovf
 aads-*.mf
 aads-*.cert
 install_vm.py
 ovf.py
 disk1.qcow2
 disk2.qcow2
 disk3.qcow2
disk4.qcow2 -
- Enter a name for the Avaya Aura® Device Services virtual machine. For example, AADS_Main.
- Press ENTER to read the EULA.
- Press Y to accept the EULA.
- Select the required Avaya Aura® Device Services profile from the following table:
ADDITIONAL INFORMATION:SpecificationsAvaya Aura® Device Services Profile 1Avaya Aura® Device Services Profile 2Avaya Aura® Device Services Profile 3Avaya Aura® Device Services Profile 4Avaya Aura® Device Services Profile 5vCPU6881012Memory910121315
- Select the Public network interfaces.
ADDITIONAL INFORMATION:ASP CLI displays the currently available network interface bridges and select the required bridge for Avaya Aura® Device Services.
- Enable or disable Enhanced Avaya Security Gateway (EASG).
ADDITIONAL INFORMATION:Important:Avaya recommends to enable EASG.ADDITIONAL INFORMATION:Note:Enable: (Recommended)By enabling Avaya Logins you are granting Avaya access to your system. This is necessary to maximize the performance and value of your Avaya support entitlements, allowing Avaya to resolve product issues in a timely manner.In addition to enabling the Avaya Logins, this product should be registered with Avaya and technically onboarded for remote connectivity and alarming. Please see the Avaya support site (support.avaya.com/registration) for additional information for registering products and establishing remote access and alarming.Disable:By disabling EASG, you are denying Avaya access to the system. This setting is not recommended as it can impact Avaya’s ability to provide support for the product. Unless the customer can manage the product, Avaya Services Logins should not be disabled.
-
Enter 1 to enable EASG.
-
Enter 2 to disable EASG.
-
- Enable or disable Data Encryption.
ADDITIONAL INFORMATION:By enabling Data Encryption, your Communication Product's Operational data, Configuration data, along with all of the Log Files will be encrypted. You will be prompted to enter a pass-phrase that will be used to create/access an encryption key. Secondly, you will be asked to configure the option for local key storage.It is important to note that the encryption of the disk may have a performance impact. For further information, contact the Administration guide(s). Before you select an encryption option, please read the Data Privacy Guideline so that you may better understand these options.ADDITIONAL INFORMATION:Enter 1 to Enable Encryption or enter 2 to Disable Encryption.
- In the Data Encryption Active field, if 1 is entered, do the following
ADDITIONAL INFORMATION:
-
In the Enter Encryption Passphrase field, enter the passphrase.
-
In the Confirm Enter Encryption Passphrase field, reenter the passphrase.
-
In the Require Encryption Passphrase at Boot-Time: (yes/no), enter the required value.
If 1 is entered, you must enter the encryption passphrase whenever the Avaya Aura® Device Services reboots.If 2 is entered, there is no need to enter the encryption passphrase whenever the Avaya Aura® Device Services reboots.ADDITIONAL INFORMATION:Important:You MUST remember the data encryption passphrase as the system prompts you to enter the encryption passphrase with every reboot of the application. If you lose the data encryption passphrase, the only option is to reinstall the OVA. -
- In the Data Encryption Active field, if 2 is entered, no action is required.
- In the Data Encryption Active field, if 1 is entered, do the following
- To configure the VM properties, enter Y in the Would you like to configure the VM properties? [y/n]: field, and continue providing the property details:
- Enter IPv4 address. For example, x.x.x.x
- Enter IPv4 Netmask. For example, m.m.m.m
- Enter IPv4 Gateway. For example, g.g.g.g
- In the AADS Hostname field, enter a valid host name or a FQDN.
ADDITIONAL INFORMATION:If a FQDN is entered, FQDN also administers the local domain name. Valid characters are, a - z, A - Z, 0 - 9, and hyphen (-).
- Optional: In the NTP Server(s) field, enter a valid NTP address or a hostname.
ADDITIONAL INFORMATION:You can type up to three NTP servers seperated by a comma.
- In the DNS Server(s) field, enter a valid DNS server IP address.
ADDITIONAL INFORMATION:You can type up to three DNS servers seperated by a comma.
- In the Search Domain List field, enter a search list of domain names. For example,mydomain.com
- To create AADS Privileged Administrator User Login, do the following:
ADDITIONAL INFORMATION:
-
In the AADS Privileged Administrator User Login, enter a privileged user name for the administrator.This is the login name for the Avaya Aura® Device Services privileged administrator.
-
In the AADS Privileged Administrator User Password field, enter a password for the Avaya Aura® Device Services privileged administrator.
-
In the Confirm AADS Privileged Administrator User Password field, reenter the password for the Avaya Aura® Device Services privileged administrator.
Note:After first login, change the Privileged Administrator password. -
- In the Do you want to set a root password?(yes/no) field, enter the required value.
- In the Power on VM automatically after deploy?: [y/n] field, enter one of the following:
-
y: Indicates Avaya Aura® Device Services virtual machine is automatically powered-on after deployment.
-
n: Indicates user has to manually power on the Avaya Aura® Device Services virtual machine on KVM cockpit.
-
- In the Proceed?[y/n] field, enter one of the following:
-
y: Avaya Aura® Device Services deployment begins.
-
n: Avaya Aura® Device Services deployment cancels.
ADDITIONAL INFORMATION:Note:Once the Avaya Aura® Device Services virtual machine is successfully deployed, ASP displays the following message: Domain creation completed. Otherwise, repeat step 3 onwards. -
- Log in to the KVM Cockpit web console as custadm in the following format: https://<IP address or FQDN of KVM host>:9090.
- If Web console is in Limited access mode, click on Turn on administrative access button.
ADDITIONAL INFORMATION:
Figure: Limited access button  ADDITIONAL INFORMATION:Note:VMs are not visible when in Limited access mode.
- For administration actions, on the top-right of the window, click on the Limited access or Turn on administrative access button.
-
Figure: Switch to administrative access 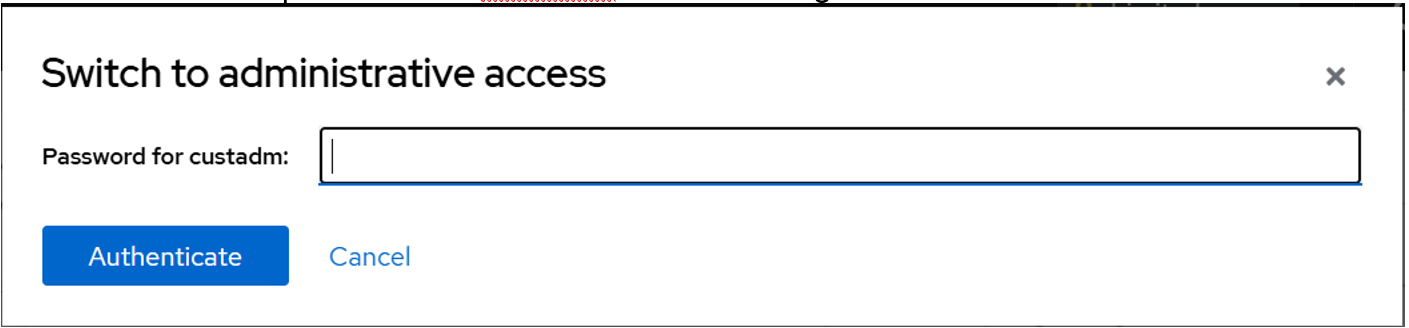
- Navigate to .
STEP RESULT:Verify that the Avaya Aura® Device Services virtual machine is deployed.
- Click on the Avaya Aura® Device Services virtual machine.
- If the Power on VM automatically after deploy?: [y/n] field is set to n, then click Run to power on the virtual machine.
ADDITIONAL INFORMATION:If the Power on VM automatically after deploy?: [y/n] field is set to y, Avaya Aura® Device Services virtual machine starts automatically.
- Click on VM Name and login from Console.
- Login to Avaya Aura® Device Services virtual machine console using privilege user credentials created in step 16.
ADDITIONAL INFORMATION:During the first login, change the privilege user password.
- In the Overview section, enable AutoStart to automatically start the virtual machine whenever the host reboots.