AVAYA DOCUMENTATION CENTER
Find answers to your technical questions and learn how to use our products
Installing the Avaya Solutions Platform 130 Series
Regenerating system SSL self-signed certificates
This procedure is only required if the IP address or FQDN/Hostname in KVM on RHEL 9.6 has been changed or modified. System SSL self-signed certificates auto-renew and have a default expiry of 395 days.
Note:
Custom CA signed SSL certificates or user generated SSL certificates take precedence over system generated SSL certificates. If either of these certificates have been previously implemented on the system, regenerating system default certificates is not required. Instead proceed to the User generated or Custom CA certificates section.
- Log in to the first KVM on RHEL 9.6 host by using a Secure Shell (SSH) client i.e. Putty (not provided by Avaya).
- Authenticate using the existing custadm credentials.
- To ensure that there are only system generated certificates, run the following commands:
ADDITIONAL INFORMATION:
cd /etc/cockpit/ws-certs.d/
 ls -lrt
In this example, the current Host self-sign certificates are displayed. The date on these is the date when certificates were issued, for example, during Host software deployment or network changes.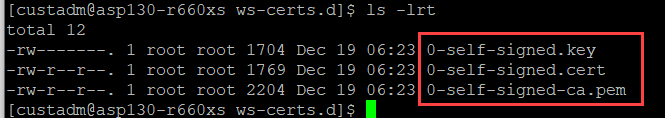
- Regenerate the certificates:
ADDITIONAL INFORMATION:
sudo rm 0-* -f
 ######[Enter password for custadm] #####
 sudo systemctl daemon-reload
 sudo systemctl restart cockpit
 ls -lrt
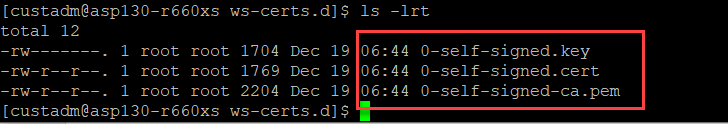
In this example, three new files starting with "0-self-signed*" are automatically generated. The date on these is current, matching maintenance activity.