AVAYA DOCUMENTATION CENTER
Find answers to your technical questions and learn how to use our products
Installing the Avaya Solutions Platform 130 Series
Validating SSL certificate expiry
During the installation of KVM on RHEL 9.6, the system generates a self-signed certificate that contains localhost|asp130-r660xs as the common name. After you configure the hostname in the system, a mismatch between the hostname and the common name in the certificate occurs.
This procedure can also be used when a user generated self-signed SSL certificate installed in Cockpit is about to or has already expired.
Note:
This activity can be conducted 100% remotely and it is a NOT service affecting procedure for the virtual machines running on the KVM on RHEL 9.6 host. Nonetheless, Avaya strongly recommends conducting this activity in a customer approved maintenance windows during off business hours when possible or low traffic hours.
Caution:
Avoid making configuration changes to the host when conducting this procedure.
Before you begin
-
Access to the ASP 130 R660xs server management network either thru a SAL Gateway connection (remotely) or direct service port connection (onsite).
-
SSH tool i.e. Putty (not provided by Avaya).
-
custadm password.
- Log in to the first KVM on RHEL RHEL 9.6 host by using a Secure Shell (SSH) client i.e. Putty (not provided by Avaya).
- Authenticate using the existing custadm credentials.
- Run the following commands to validate current SSL certificate expiry:
ADDITIONAL INFORMATION:
cd /etc/cockpit/ws-certs.d/
 ls -lrt
 openssl x509 -in <*selfsigned.cert*> -noout -text | grep "Not After"
Note:The 0-self-signed.cert certificate, is the default, system auto-generated certificate that gets installed during the KVM on RHEL installation. The same command can be executed for other certificates (if present) if the default one has been re-generated.Example:openssl x509 -in 0-self-signed.cert -noout -text | grep "Not After"[custadm@asp130-r660xs /]$ cd /etc/cockpit/ws-certs.d/
[custadm@asp130-r660xs ws-certs.d]$ ls -lrt
total 12
-rw-------. 1 root root 1704 Aug 11 07:21 0-self-signed.key
-rw-r--r--. 1 root root 1769 Aug 11 07:21 0-self-signed.cert
-rw-r--r--. 1 root root 2204 Aug 11 07:21 0-self-signed-ca.pem
[custadm@asp130-r660xs ws-certs.d]$ openssl x509 -in 0-self-signed.cert -noout -text | grep "Not After"
Not After : Sep 10 13:21:08 2027 GMT
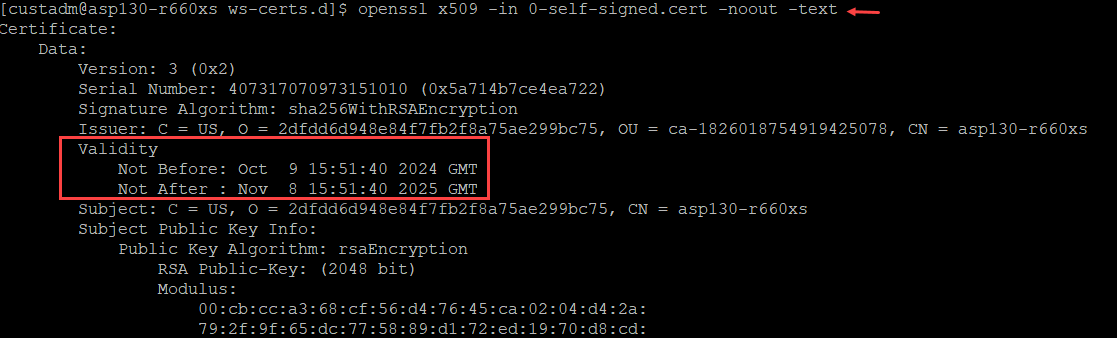
Or to see full certificate chain:openssl x509 -in 0-self-signed.cert -noout -text[custadm@asp130-r660xs ws-certs.d]$ openssl x509 -in 0-self-signed.cert -noout -text
Certificate:
Data:
Version: 3 (0x2)
Serial Number: 7257409270247857624 (0x64b77f47a6c01dd8)
Signature Algorithm: sha256WithRSAEncryption
Issuer: C=US, O=d023229cbb5a48468806657ea9db89d7, OU=ca-2068271267134422656, CN=asp130-r660xs.acp.avaya.com
Validity
Not Before: Aug 11 13:21:08 2026 GMT
Not After : Sep 10 13:21:08 2027 GMT
Subject: C=US, O=d023229cbb5a48468806657ea9db89d7, CN=asp130-r660xs.acp.avaya.com
Subject Public Key Info:
Public Key Algorithm: rsaEncryption
Public-Key: (2048 bit)
- If the “Not After” date displayed is older than the current KVM on RHEL 9.6 host date, proceed with re-generating the SSL Self-signed Certificate.
ADDITIONAL INFORMATION:Output example:
Machine Date:
  Thu Jul 22 13:07:12 UTC 2024
  Validity
             Not Before: Jul 19 13:40:14 2023 GMT
             Not After : Jul 19 13:40:14 2024 GMT
Or to see full certificate chain:openssl x509 -in 0-self-signed.cert -noout -text